How HSM Solutions and Database Encryption Solutions Work Together to Protect Data
Introduction
Databases store some of the most valuable information within an organization. Customer details, financial records, employee information, business documents, transaction data, and confidential operational records often reside inside databases.
This makes databases an attractive target for cybercriminals. Organizations need strong security controls to prevent unauthorized access and protect information if attackers compromise part of their infrastructure.
Database encryption provides an important layer of protection. It converts readable information into an encrypted format that unauthorized users cannot easily understand. However, encryption depends on cryptographic keys, and those keys require secure storage and management.
This is where HSM Solutions and database encryption solutions work together.
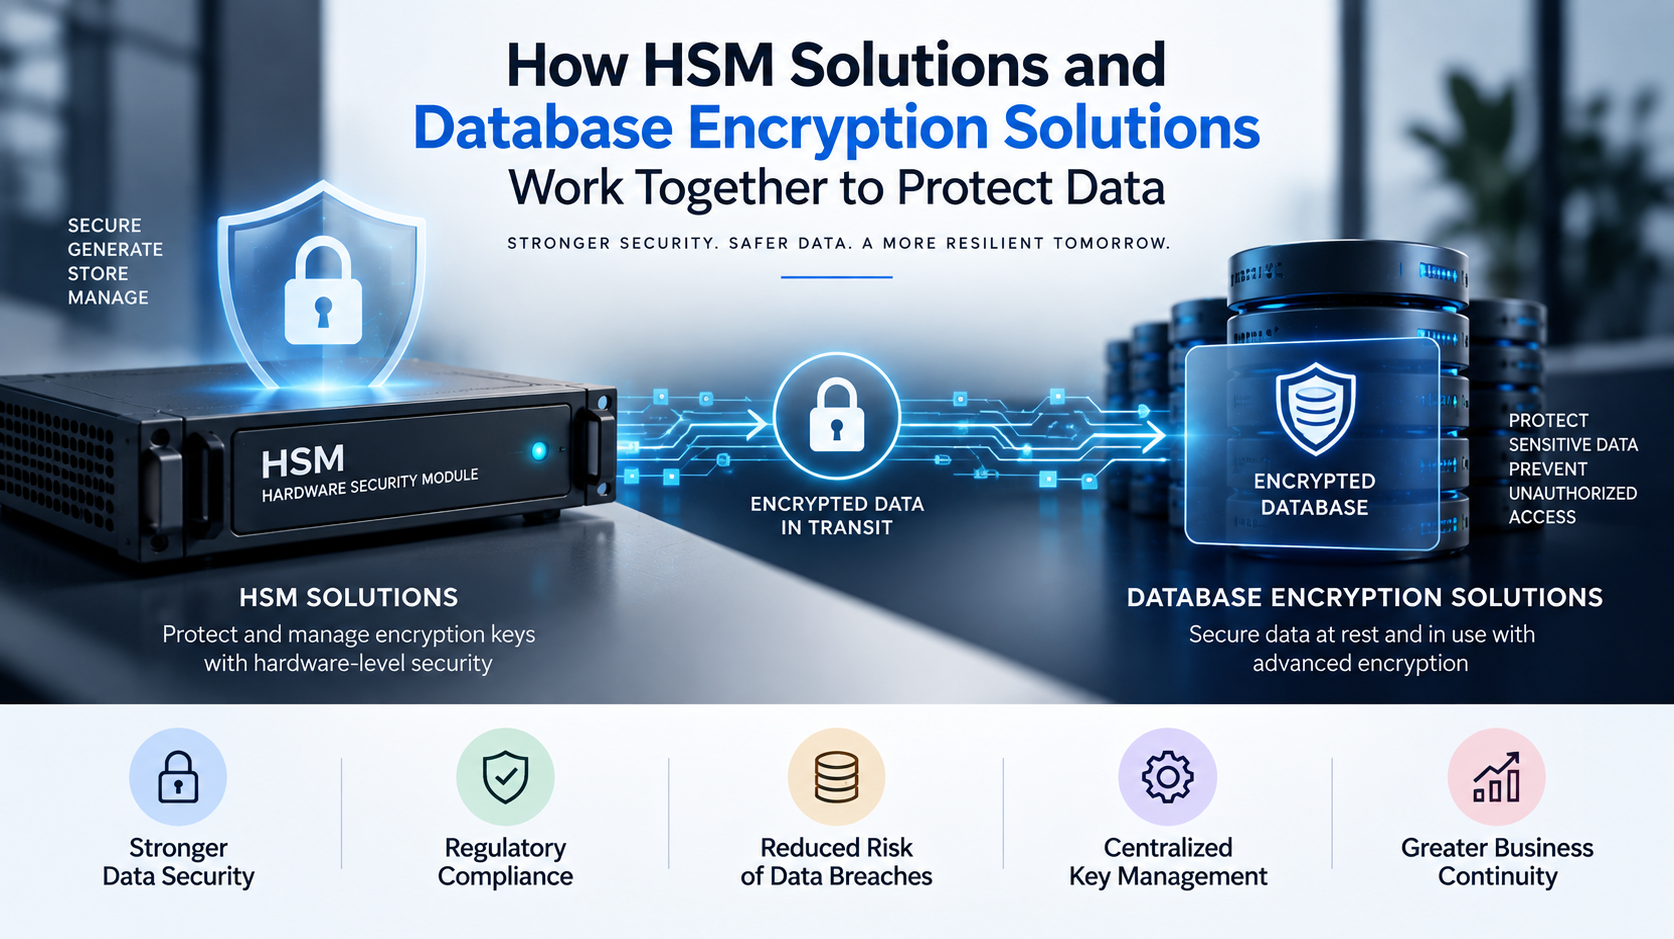
HSM technology provides a secure environment for protecting cryptographic keys, while database encryption protects the data itself. Effective Key management connects these two security layers and helps organizations control the encryption key lifecycle.
Understanding Database Encryption
Database encryption protects information stored within a database by converting readable data into ciphertext.
Organizations can use different encryption approaches depending on their requirements and database architecture.
Common approaches include:
- Transparent Data Encryption
- Column-level encryption
- Application-level encryption
- File-level encryption
Each method provides different security and operational characteristics.
A database encryption solution can help protect sensitive information from unauthorized access. However, organizations must carefully manage the keys used by the encryption system.
Why Encryption Keys Need Separate Protection
Encryption keys are highly sensitive security assets. If attackers obtain both encrypted data and the corresponding keys, encryption may no longer provide meaningful protection.
For this reason, organizations should avoid treating encryption keys like ordinary database information.
A strong architecture separates encrypted information from the systems that protect its keys.
This is one reason organizations use HSM modules. HSM technology can protect cryptographic keys inside specialized hardware while allowing authorized systems to perform approved operations.
What Are HSM Solutions?
HSM Solutions provide technologies designed to protect cryptographic keys and perform sensitive cryptographic operations within secure hardware environments.
HSMs can support:
- Key generation
- Key storage
- Encryption
- Decryption
- Digital signing
- Authentication
- Certificate management
The hardware-based approach adds a security layer between sensitive cryptographic keys and the broader IT environment.
If an application server becomes compromised, attackers may not automatically gain direct access to the keys protected inside the HSM.
How Database Encryption and HSM Technology Work Together
A database encryption architecture can use encryption to protect information while using HSM technology to protect the encryption keys.
The basic process works like this:
Sensitive data → Encryption → Encrypted database → Protected encryption key → HSM
When an authorized application needs access to encrypted data, it can request the required cryptographic operation according to the configured security policies.
The HSM performs or supports the cryptographic operation without unnecessarily exposing the underlying key.
This architecture creates separation between the data and its cryptographic protection.
The Role of Key Management in the Architecture
Key management provides the processes required to control encryption keys throughout their lifecycle.
An organization needs to know:
- When a key was created
- Which data it protects
- Which applications can use it
- Who can administer it
- When it should rotate
- When it should expire
- How it should be retired
Key management in cryptography provides the framework for handling these requirements.
Without proper lifecycle management, organizations can accumulate unused keys, lose track of ownership, or fail to rotate keys according to policy.
How HSM Modules Protect Database Encryption Keys
HSM modules can protect encryption keys used by databases and other enterprise applications.
They can generate keys inside a controlled hardware environment and prevent unauthorized extraction.
HSM modules can also provide controlled access to cryptographic functions.
For sensitive databases, this approach can reduce the risk associated with storing keys directly alongside application data.
Organizations should select HSM configurations based on their security requirements, application architecture, availability needs, and compliance obligations.
Supporting Cloud Database Environments
Many organizations now use cloud-hosted databases. Cloud migration creates new considerations for encryption and Key management.
Businesses need to protect data while maintaining appropriate control over cryptographic keys.
HSM Solutions can support cloud and hybrid architectures by providing secure key protection and integration capabilities.
Organizations should define clear responsibilities between their internal security teams and cloud service providers. They should also understand where keys reside, which systems can use them, and how key lifecycle operations work.
Thales Key Management for Enterprise Encryption
Thales key management can help organizations centralize control over cryptographic keys across different environments.
Enterprises may use encryption across databases, cloud platforms, applications, and file systems. Centralized management can simplify administration and provide better visibility.
When integrated with appropriate HSM infrastructure, Thales key management can support a security architecture where organizations maintain stronger control over critical cryptographic assets.
Businesses should evaluate the capabilities of any key management solution against their specific technical and compliance requirements.
Database Encryption and Data Security Standards
Organizations often need to follow applicable Data security standards when protecting sensitive information.
Encryption and secure key management can support requirements related to data confidentiality, access control, auditability, and security governance.
However, database encryption should form part of a wider security program.
Organizations should also implement:
- Strong authentication
- Access controls
- Network security
- Security monitoring
- Vulnerability management
- Backup protection
- Incident response
A database encryption solution works best when organizations integrate it with these broader controls.
Practical Benefits of Combining HSM and Database Encryption
Stronger Key Protection
HSM technology provides a dedicated environment for protecting cryptographic keys.
Better Separation of Data and Keys
Organizations can keep encryption keys separate from the databases they protect.
Improved Access Control
Security teams can restrict cryptographic operations to authorized systems and users.
Support for Compliance
Organizations can demonstrate stronger controls around encryption and key management.
Greater Scalability
Centralized HSM Solutions can support growing numbers of applications and databases.
Reduced Key Exposure
Hardware-based protection reduces the need to expose sensitive cryptographic keys to application environments.
Best Practices
Organizations should follow several practices when combining database encryption with HSM technology.
Classify Sensitive Data
Identify which database fields and records require encryption.
Select Appropriate Encryption Methods
Choose encryption based on the sensitivity of the information and application requirements.
Protect Keys Separately
Keep critical encryption keys in an appropriately secured environment.
Automate Lifecycle Operations
Automate rotation and other routine Key management processes where possible.
Monitor Cryptographic Activity
Review key usage and investigate unexpected operations.
Test Recovery Procedures
Organizations should test their ability to recover critical keys and restore encrypted data safely.
Conclusion
Database encryption protects sensitive information, but secure encryption depends on effective key protection. Organizations therefore need to treat database security and cryptographic Key management as connected requirements.
HSM Solutions provide hardware-based protection for cryptographic keys, while a database encryption solution protects information stored within databases. HSM modules can strengthen this architecture by providing a controlled environment for key generation, storage, and cryptographic operations.
Effective key management in cryptography ensures that organizations control the complete key lifecycle. Technologies such as Thales key management can provide centralized capabilities for managing encryption keys across enterprise systems.
By combining database encryption, HSM technology, Key management, access controls, monitoring, and appropriate Data security standards, organizations can create a stronger and more structured approach to protecting sensitive business data.

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek