Continuous Security Testing: Why Annual Penetration Testing Is No Longer Enough
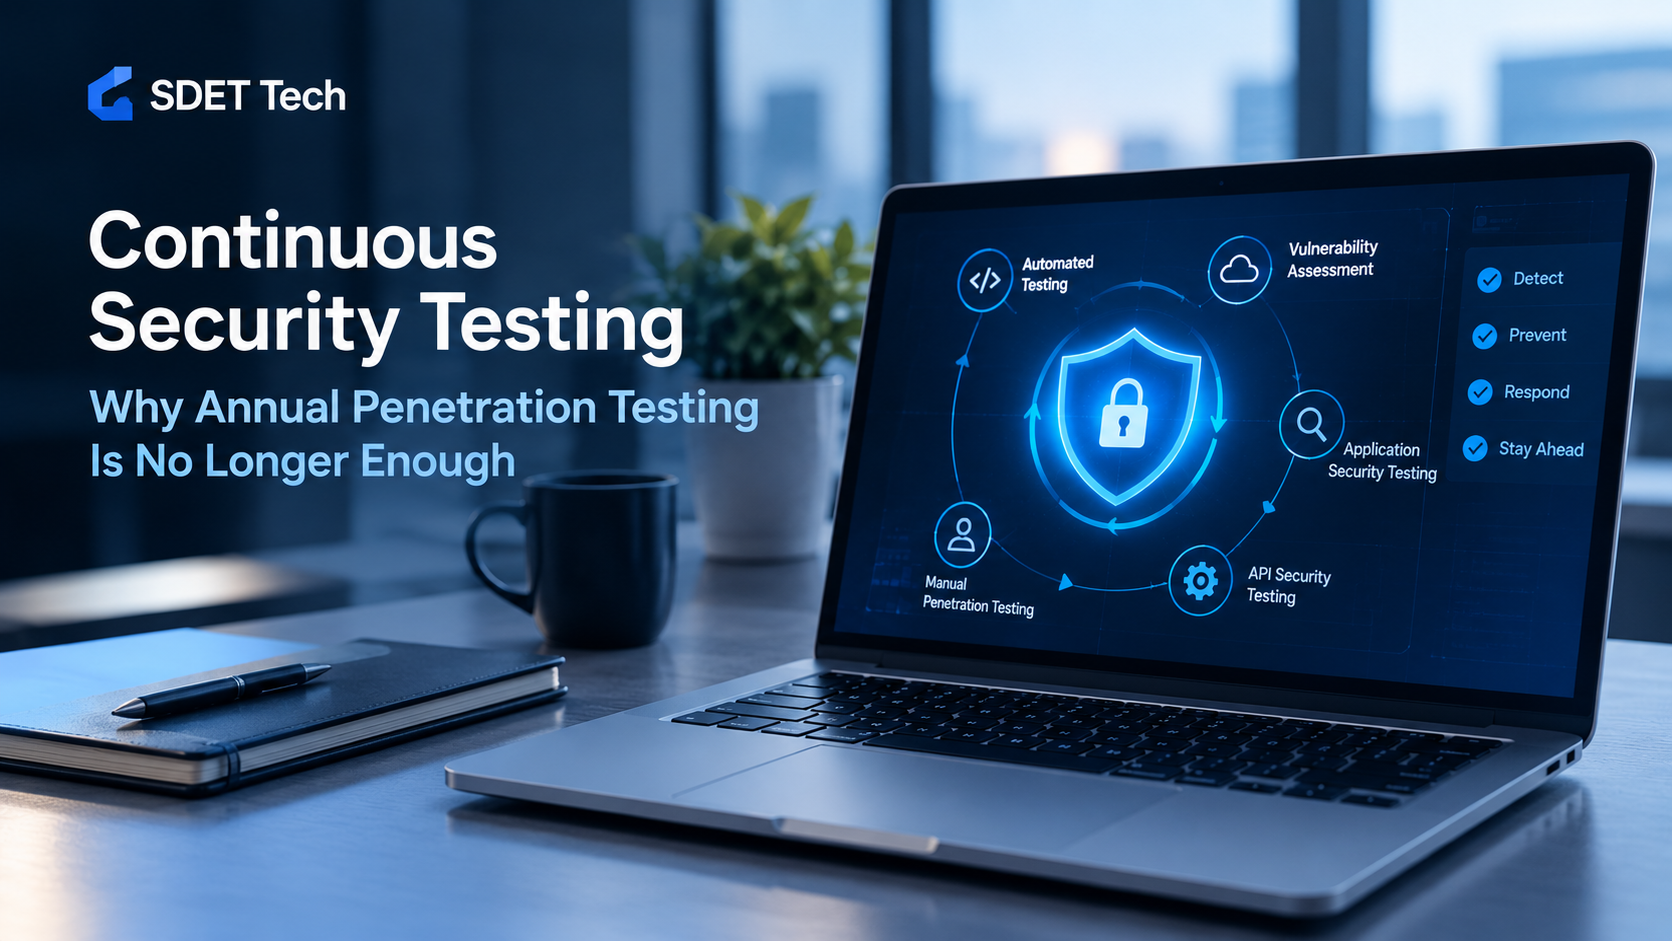
Cyber threats evolve faster than traditional security testing cycles. An annual penetration test can identify vulnerabilities at a specific point in time, but modern applications are continuously changing through new releases, APIs, cloud deployments, third-party integrations, and infrastructure updates. This is why continuous security testing is becoming an important part of modern cybersecurity strategies for businesses across the US.
What Is Continuous Security Testing?
Continuous security testing is an ongoing approach to identifying, validating, and monitoring security vulnerabilities throughout the software development lifecycle. Instead of relying only on a yearly penetration test, organizations continuously evaluate applications, APIs, infrastructure, and new code for potential security weaknesses.
Continuous penetration testing, automated security testing, vulnerability scanning, and manual security assessments can work together to provide broader security coverage.
Why Annual Penetration Testing Has Limitations
An annual penetration test provides valuable insights but represents a limited snapshot of an application's security posture. A website or application tested in January may have significant changes by June.
New vulnerabilities can emerge after an assessment. Developers may introduce new code. APIs can change. Cloud configurations can be modified. New third-party services can be integrated. Each change can introduce additional security risks.
This creates a gap between the time a vulnerability is introduced and the next scheduled security assessment.
How Continuous Security Testing Helps
A continuous approach integrates security testing into the software development lifecycle. Security teams and QA teams can test applications more frequently and identify vulnerabilities earlier.
Key components can include:
Automated security testing: Automated vulnerability scans can regularly evaluate applications and infrastructure for common security weaknesses.
Application security testing: Web applications and mobile applications can be tested for vulnerabilities involving authentication, authorization, input validation, session management, and data exposure.
API security testing: Continuous API security testing helps identify weaknesses in authentication, authorization, access controls, and exposed endpoints as APIs evolve.
Continuous vulnerability assessment: Regular vulnerability assessments help organizations maintain better visibility into changing security risks.
Manual penetration testing: Expert penetration testers can investigate complex vulnerabilities, business logic flaws, and attack scenarios that automated tools may not identify effectively.
Continuous Security Testing for US Businesses
For US businesses handling customer information, financial data, healthcare information, or other sensitive data, maintaining a strong application security program is increasingly important. Continuous cybersecurity testing can help organizations identify weaknesses before attackers exploit them and support broader security and compliance objectives.
Rather than replacing penetration testing, continuous security testing complements traditional penetration testing services by providing more frequent security validation between formal assessments.
Build a Stronger Security Testing Strategy
Modern software development requires security to be tested throughout the application lifecycle. Combining continuous security testing, automated vulnerability testing, API security testing, application security testing, and expert penetration testing can provide a more comprehensive approach to identifying security weaknesses.
SDET Tech provides cybersecurity testing services designed to help businesses identify vulnerabilities across applications and digital environments. By integrating security testing into development and release processes, organizations can improve their security posture and respond to vulnerabilities more proactively.
Continuous testing means security does not have to wait for the next annual penetration test.

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Greek