


Strengthen Data Center Security Across Oman
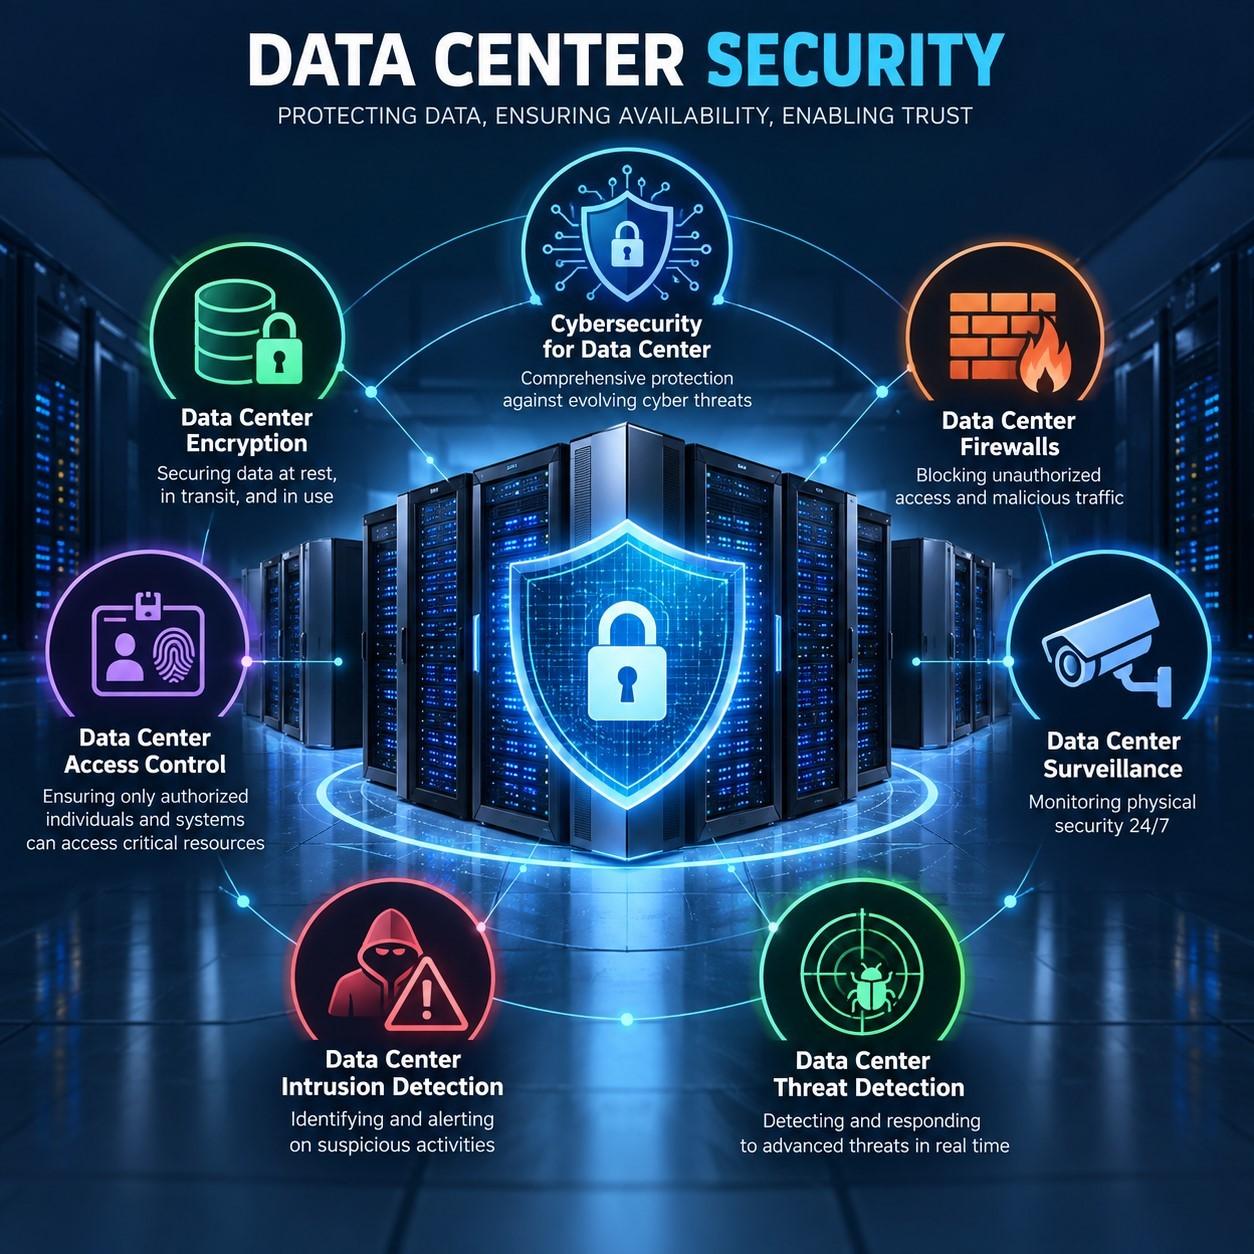
Oman's push toward a diversified, technology-driven economy under Oman Vision 2040 is bringing a new generation of data centres online across Muscat, Salalah, and the Duqm Special Economic Zone, and every one of them depends on genuinely robust Data Center Security. As government cloud initiatives, banking systems, and international colocation tenants increasingly host workloads inside the Sultanate, a single physical intrusion or breach can carry consequences well beyond the operator's own balance sheet.
This guide walks through the physical and digital layers that make up a modern data centre security programme in Oman, what regulators and enterprise tenants now expect, and how facility operators can plan a defence that scales as the country's digital infrastructure continues to grow.
Why Oman's Growing Digital Economy Raises the Security Stakes
Oman's National Broadband Strategy and its wider digital transformation agenda have accelerated investment in data centre capacity across the Sultanate, with government cloud migration and private-sector digitisation both driving demand for local hosting rather than relying solely on facilities abroad. That local concentration of sensitive workloads makes Omani facilities a more attractive target for both physical intruders and cyber actors than in years past, when far less critical data was hosted domestically.
Enterprise tenants are responding accordingly. Banks, telecom operators, and government entities considering colocation space in Oman increasingly request documented proof of both physical and digital security controls before signing a contract, making security posture a genuine differentiator between competing facilities rather than an assumed baseline.
Building Cybersecurity for Data Center Environments from the Network Up
Physical barriers alone cannot protect a facility that is, at its core, a dense concentration of networked compute and storage. Cybersecurity for Data Center operations cover everything from network segmentation between tenant environments to hardened management interfaces on the building's own physical security systems, since a poorly secured camera or access controller can itself become an entry point into the wider network.
A mature programme treats the facility's operational technology, cameras, door controllers, environmental sensors, as part of the same attack surface as the servers themselves, applying the same patching discipline, network isolation, and monitoring that the IT side of the business already expects from its production systems.
Data Center Encryption as the Last Line of Defence
Even with strong perimeter and network controls, a defence-in-depth strategy assumes that some layer will eventually be tested. Data Center Encryption protects data at rest on storage arrays and in transit between racks, ensuring that even a successful intrusion into a storage system does not hand an attacker usable, readable information.
For facilities hosting regulated data, financial records, health information, or government workloads, encryption is increasingly a contractual requirement from tenants rather than a discretionary hardening measure, with key-management practices, hardware security modules, and rotation policies now routinely reviewed during tenant security audits before a lease is signed.
Data Center Firewalls and Network Segmentation Between Tenants
In a multi-tenant colocation facility, the single most important network control is making sure one tenant's environment cannot see or affect another's. Data Center Firewalls enforce that segmentation, filtering traffic between tenant zones, management networks, and the wider internet according to strict, auditable rule sets rather than relying on flat network architecture.
Modern facility-grade firewall deployments also incorporate intrusion-prevention capabilities directly into the traffic-filtering layer, catching known attack signatures in real time rather than relying solely on downstream detection tools to flag suspicious activity after it has already reached a tenant's environment.
Data Center Access Control for Physical Perimeter Protection
No amount of network hardening compensates for an unlocked server-room door. Data Center Access Control governs who can physically enter a facility, and increasingly which specific rack or cage within it, using layered credentials that typically combine biometric verification, card access, and mantrap or interlock doors that prevent more than one person passing through on a single authorised entry.
Facilities pursuing Tier III or Tier IV certification, or those hosting government and financial tenants, typically implement at least three distinct access layers: perimeter fencing and gatehouse verification, building-entry biometric checks, and cage or rack-level access restricted to only the specific staff authorised for that tenant's equipment.
Common Layered Access Zones in an Omani Facility
● Outer perimeter: vehicle gates, fencing, and gatehouse identity verification for anyone entering the site.
● Building entry: biometric and multi-factor checks at the main facility doors, logged and time-stamped automatically.
● Data hall and cage level: restricted access limited to specific tenant staff, often requiring a second authorised escort for visitors.
Data Center Surveillance Coverage That Leaves No Blind Spots
Access control tells a facility who is authorised to be somewhere; Data Center Surveillance provides the visual record confirming what actually happened at every checkpoint, corridor, and rack aisle. Comprehensive camera coverage across entry points, loading docks, and internal aisles gives security teams both a real-time monitoring capability and a forensic record that colocation tenants frequently request as part of their own compliance reviews.
Modern facility camera systems increasingly incorporate video analytics that flag loitering near restricted cages, tailgating attempts at mantrap doors, or unattended equipment left in a corridor, giving a lean on-site security team the same coverage that would otherwise require dozens of staff watching monitor walls around the clock.
Data Center Intrusion Detection Across Physical and Network Layers
A truly layered facility treats intrusion detection as both a physical and a digital discipline. Data Center Intrusion Detection on the physical side covers perimeter fence sensors, door-forced-open alarms, and vibration or motion sensors around sensitive equipment, while its network counterpart monitors traffic patterns for the kind of anomalous behaviour that signals a compromised system inside the facility's own infrastructure.
Integrating both disciplines into a single monitoring console, rather than running physical security and network security teams as entirely separate operations, shortens the time between an intrusion attempt and a coordinated response, which matters enormously when an incident could involve someone physically present at a rack alongside a simultaneous network anomaly.
Data Center Threat Detection and Round-the-Clock Monitoring
Detection only has value if it feeds a monitoring operation capable of acting on it immediately. Data Center Threat Detection platforms correlate signals from cameras, access logs, network sensors, and environmental monitoring into a single operational picture, flagging genuine anomalies for a human operator rather than burying security teams under thousands of low-priorities alerts each day.
For Omani facilities running a 24/7 security operations centre, the goal is reducing alert fatigue without missing a genuine incident, which typically means investing in correlation and prioritisation logic rather than simply adding more raw sensor data to an already overwhelmed monitoring team.
Regulatory Expectations Shaping Facility Design in Oman
Data centre operators in Oman increasingly design security programmes around a combination of international standards and local regulatory expectations, since many enterprise and government tenants will only sign with facilities that can demonstrate a recognised compliance posture rather than take security claims at face value.
Oman's Personal Data Protection Law, issued under Royal Decree 6/2022, sets requirements for the lawful collection, storage, and processing of personal data, which extends directly to how a data centre must handle access logs, surveillance footage, and any personal information tied to enrolled staff or visitors. Facilities also commonly align with ISO 27001 for information security management and, where payment data is processed, PCI DSS, while those pursuing government or financial-sector tenants typically align their physical security zoning with Uptime Institute Tier III or Tier IV criteria.
Incident Response Planning for a Layered Facility
Detection and prevention only deliver value if a facility has a rehearsed response plan behind them. A well-run Omani data centre treats incident response as a documented, tested process rather than an assumption that staff will improvise correctly during a genuine emergency.
● A defined escalation chain so a physical intrusion alert reaches both security and IT operations simultaneously, not sequentially.
● Pre-agreed tenant communication procedures, since colocation tenants expect prompt, accurate notification if their specific cage or environment is affected.
● Regular tabletop exercises simulating both physical breach and network intrusion scenarios, tested together rather than in isolation.
● Post-incident review procedures that feed lessons learned back into access policies and monitoring rules, rather than closing the ticket and moving on.
Facilities that rehearse this process before an actual incident consistently recover faster and retain tenant confidence more effectively than those treating their response plan as a document that exists only for audit purposes.
Tektronix Experience Securing Data Center Security Oman Facilities
Tektronix has worked with colocation operators, enterprise IT teams, and facility managers across Oman and the wider GCC to design layered perimeter and access security for data centre environments, ranging from single-tenant enterprise server rooms to multi-tenant colocation halls supporting government and private-sector clients.
That experience across facilities with genuinely different risk profiles, a bank's private server room carries different requirements from a public cloud colocation hall, is what separates a properly engineered Data Center Security Oman deployment from a generic commercial security fit-out. Every project is planned around the facility's certification goals, tenant mix, and existing IT architecture before any hardware is specified.
Facility operators evaluating vendors for this category can review Tektronix dedicated data centre perimeter security solutions page, which outlines access control, surveillance, and perimeter protection approaches used across the region.
Planning Data Center Security Muscat Facilities Need for Certification
Muscat's growing cluster of government-adjacent and enterprise data centres, concentrated around the capital's business districts and the Knowledge Oasis Muscat technology park, often needs to satisfy stricter certification and audit requirements than a typical regional facility, given the concentration of public-sector and financial workloads increasingly hosted in the capital. A Data Center Security Muscat deployment should be planned with Tier III or Tier IV uptime and security requirements in mind from the earliest design stage, rather than retrofitting compliance features after construction is complete.
Facility planning teams should confirm early whether their target tenant base requires specific audit certifications, since designing access-control zoning and surveillance coverage around those requirements from day one is significantly cheaper than reconfiguring a live facility later. Operators ready to plan a deployment can consult Tektronix data centre security integration page for a site-specific assessment.
Conclusion
Oman's expanding digital economy is placing growing amounts of sensitive data inside its own borders, and a properly layered Data Center Security programme is what keeps that trust intact. From encrypted storage and segmented Data Center Firewalls to biometric Data Center Access Control and correlated Data Center Threat Detection, operators that plan every layer around their certification goals and tenant mix build facilities that scale safely as the Sultanate's digital infrastructure continues to grow.
FAQs
1. What is the difference between physical and cybersecurity layers in a data centre?
Physical Data Center Security covers perimeter fencing, access control, and surveillance, while Cybersecurity for Data Center operations protects the network, servers, and management systems from digital intrusion. A properly designed facility integrates both rather than treating them as separate concerns.
2. Why do colocation tenants ask about encryption before signing a lease in Oman?
Enterprise tenants increasingly require proof of Data Center Encryption for data at rest and in transit as part of their own regulatory and audit obligations, particularly banks and government entities subject to Oman's data-protection requirements.
3. How many layers of access control does a Tier III or Tier IV facility typically need?
Most certified facilities implement at least three layers of Data Center Access Control: perimeter gatehouse verification, biometric building entry, and restricted cage or rack-level access limited to authorised tenant staff.
4. Can surveillance systems reduce the need for large on-site security teams?
Yes. Modern Data Center Surveillance platforms use video analytics to flag tailgating, loitering, and unattended equipment automatically, giving a smaller on-site team the coverage that would otherwise require many more staff watching monitors manually.
5. What causes alert fatigue in data centre threat monitoring, and how is it fixed?
Alert fatigue happens when raw sensor data is pushed to operators without prioritisation. Effective Data Center Threat Detection and Data Center Intrusion Detection platforms correlate signals across systems first, surfacing only genuine anomalies so security teams can respond quickly instead of sorting through thousands of low-priority notifications.

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Greek
